Senior Information Security Consultant

SECURITY
WITHOUT
BLIND SPOTS.

Offensive Security × Architecture × AI Security

I work across offensive security, application security, network security architecture, vulnerability management, governance, and AI security — then turn technical findings into practical decisions for engineering and leadership teams.
Web / API / MobileSource Code ReviewNetwork ArchitectureRed TeamingAI / LLM SecurityRisk & DLP
4+Years Experience
06Practice Areas
07Certifications
∞Curiosity Driven
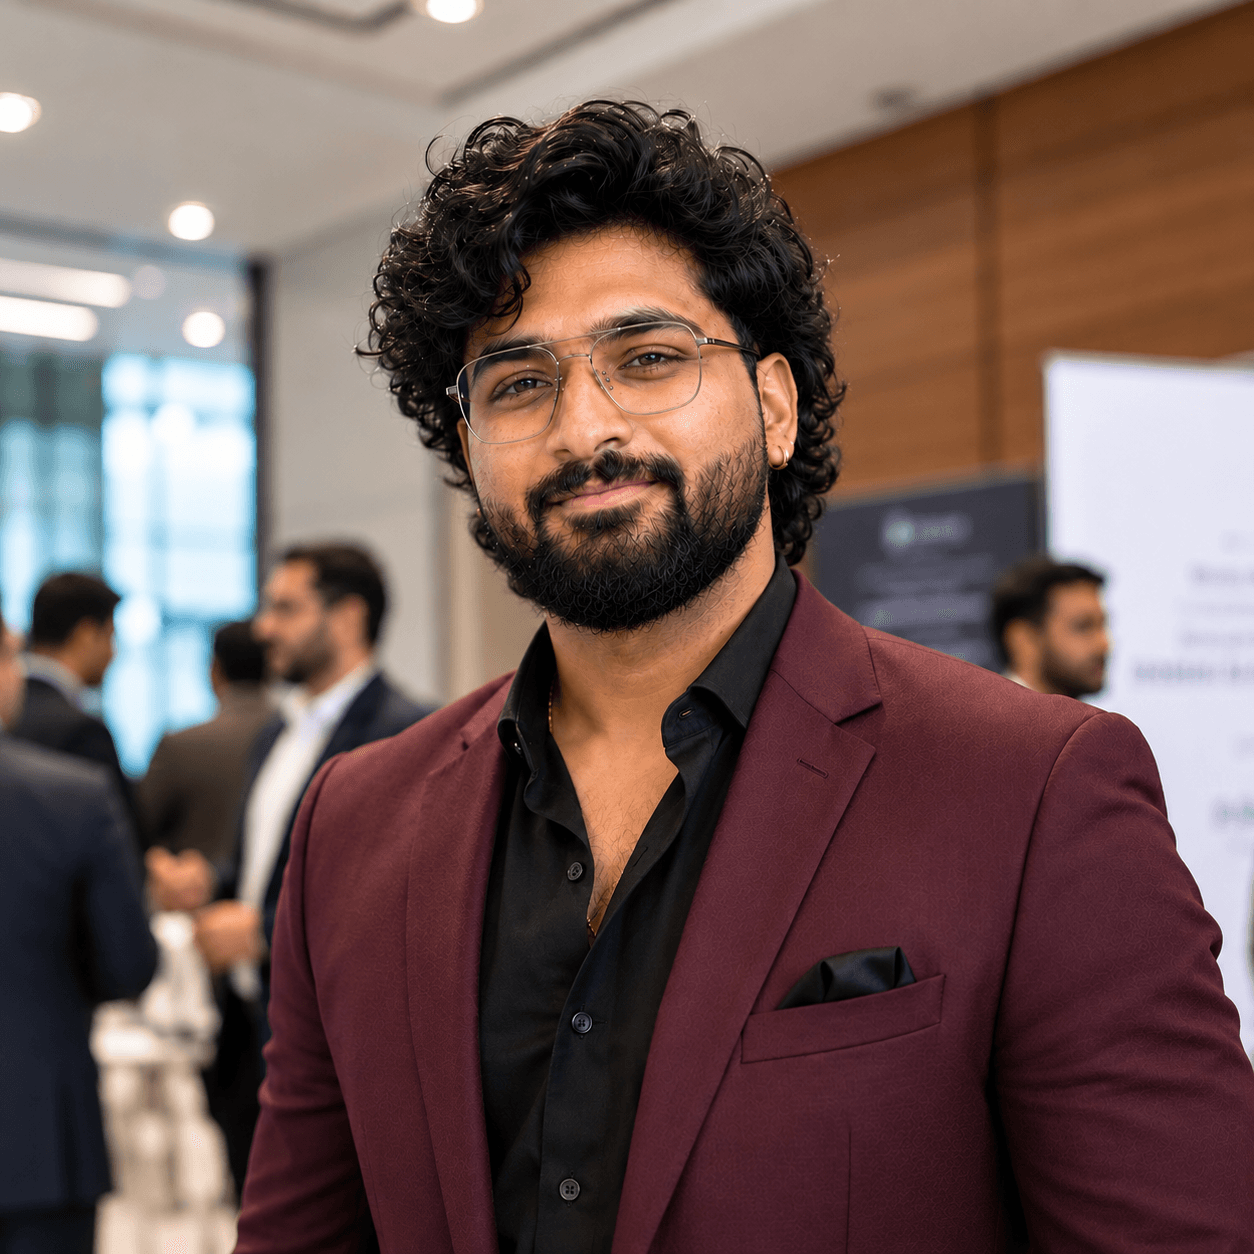
Harshad Pawar
SECURITY / RESEARCH / ADVISORYMumbai, India
⌁
◈
✦

Broad enough to advise.
Technical enough to test.

01

Offensive Security

Web, API, mobile, thick client, network, IoT and red-team style assessments.

WebAPIMobileThick ClientNetworkIoTRed Teaming
02

Application Security

Source-code review, SAST/SCA, secure SDLC and application design review.

Source Code ReviewSASTSCASecure SDLCApplication Architecture
03

Security Architecture

Network architecture, segmentation, security design, trust boundaries and threat modeling.

Network Architecture ReviewSecurity Design ReviewSegmentationThreat Modeling
04

Vulnerability Management

Exposure management, VA, remediation tracking, metrics and technical reporting.

VAExposure ManagementRemediationMetricsTracking
05

Governance & Risk

DLP, risk assessment, audit support, compliance alignment and security governance.

DLPRisk AssessmentAudit SupportComplianceSecurity Governance
06

AI Security

LLM security, prompt injection, RAG security, agent security, data leakage and AI red teaming.

LLM SecurityPrompt InjectionRAG SecurityAgent SecurityAI Red TeamingData Leakage

Professional experience
with technical depth.

Apr 2025 — Aug 2026

Cyber Security Consultant

ProTechmanize · Full-time

Thane, Maharashtra, India · On-site

01

Cybersecurity Consultant deployed at Aditya Birla Capital, delivering offensive security and application security engagements across enterprise environments.

  • Conducted Web, API, and Mobile Application Penetration Testing for critical business applications.
  • Performed Secure Source Code Reviews to identify and validate security vulnerabilities.
  • Executed Red Team engagements to assess the organization’s real-world security posture.
  • Managed and secured CI/CD pipelines, integrating security practices into the software development lifecycle (DevSecOps).
  • Supported and handled RBI Security Audit activities, including security assessments, remediation validation, and compliance coordination.
Jan 2023 — Mar 2025

Associate

Asynk · Full-time

India · Remote

02
  • Performed Vulnerability Assessments (VA) to identify and prioritize security weaknesses.
  • Conducted Web Application Penetration Testing for enterprise and customer-facing applications.
  • Executed API Penetration Testing to assess authentication, authorization, and business logic vulnerabilities.
  • Performed Mobile Application Penetration Testing on Android and iOS applications.
  • Conducted Network Penetration Testing across internal and external infrastructure.
  • Performed Secure Source Code Reviews to identify security flaws and provide remediation recommendations.
Nov 2022 — Dec 2022

Intern

KaaShiv InfoTech · Internship

Mumbai, Maharashtra, India · Remote

03
Aug 2021 — Sep 2021

Intern

Verzeo · Internship

Mumbai, Maharashtra, India · Remote

04

Technical work worth
publishing properly.

FEATURED BLOG

Before the AI Answers: Testing Customer Data Isolation in a Banking RAG Pipeline

Can a banking AI assistant retrieve useful information without exposing another customer’s records? A controlled experiment explores how access filtering affects data privacy and retrieval coverage in a RAG pipeline.

Read full article →
Lab Note · ResearchTesting Customer Data Isolation in a Banking RAG PipelineOpen →
Blog · AI SecurityAI Security in Banking and NBFCsOpen →
Blog · SecurityHow to Get Into Cybersecurity: A Comprehensive Roadmap. Open →
Lab Note

Testing Customer Data Isolation in a Banking RAG Pipeline

A Python experiment comparing three retrieval designs to examine how access filtering affects customer privacy and the availability of relevant records.

Blog

Before the AI Answers: Testing Customer Data Isolation in a Banking RAG Pipeline

Can a banking AI assistant retrieve useful information without exposing another customer’s records? A controlled experiment explores how access filtering affects data privacy and retrieval coverage in a RAG pipeline.

AI SecurityRead article →
Blog

AI Security in Banking and NBFCs

How can banks and NBFCs use AI to strengthen cybersecurity while defending against AI-powered threats? Explore deepfake fraud, prompt injection, data leakage and AI agent security, with practical controls, a secure loan-review workflow and a 90-day adoption plan.

AI SecurityRead article →
Blog

How to Get Into Cybersecurity: A Comprehensive Roadmap.

Open the article to read more.

Blog

Episode 2: The Art of Recon - Finding What Others Miss

Open the article to read more.

Blog

Pickle Rick: CTF Challenge | Write-Up

Open the article to read more.

Major certifications up front.
More in a slider.

CRT
Major
Certified Red Team Operator

CRTO

Zero Point Security

Core credential01
EJP
Major
eLearnSecurity Junior Penetration Tester

eJPT

INE

Core credential02
CEH
Major
Certified Ethical Hacker

CEH

EC-Council

Core credential03
CRT
Additional
Certified Red Team Analyst

CRTA

CyberWarFare Labs

Specialization04
CRT
Additional
CRTOM

Red Team Leaders

Specialization05
CSC
Additional
CSCRB

Red Team Leaders

Specialization06
AI
Additional
Certified LLM Security Expert

LLM

Red Team Leaders

Specialization07

Have a security problem
worth solving?

For opportunities, consulting, security research collaboration, technical discussions or speaking requests — send me a message.

Emailharshadpawar69@gmail.com
LocationMumbai, India
FocusSecurity roles · Consulting · Research
Your message is sent server-side when email delivery is configured.